
DNA: updated from administration.md
Root ·
Updated from docs/dna/administration.md in the Knowen repository: How Knowen works is kept with the code.
Changes to the content
# How Knowen is run **Two roles, held by people.** Knowen is looked after by people who hold one or both administration roles: - **Root** decides where no one else does: at the top level of the public graph, for nodes with no owner on record, and on changes no owner has answered for a day (see [Owners decide](dna:owners-decide/nodes/29512)). Root also sees the whole Reviewing queue, so nothing is held up. - **System management** looks after accounts: plans, limits, sign-ups, confirming emails, and who holds which role. Several people may hold each role. The Root account (@root) holds both. **Acting in a role.** Someone who holds a role switches to it from the account menu, under **Role**, and back to **Yourself**. As Root, everything they do is done by the Root account and shows as **Root**, never their own name or handle. A strip under the top bar says which role is on, with **Switch back**. 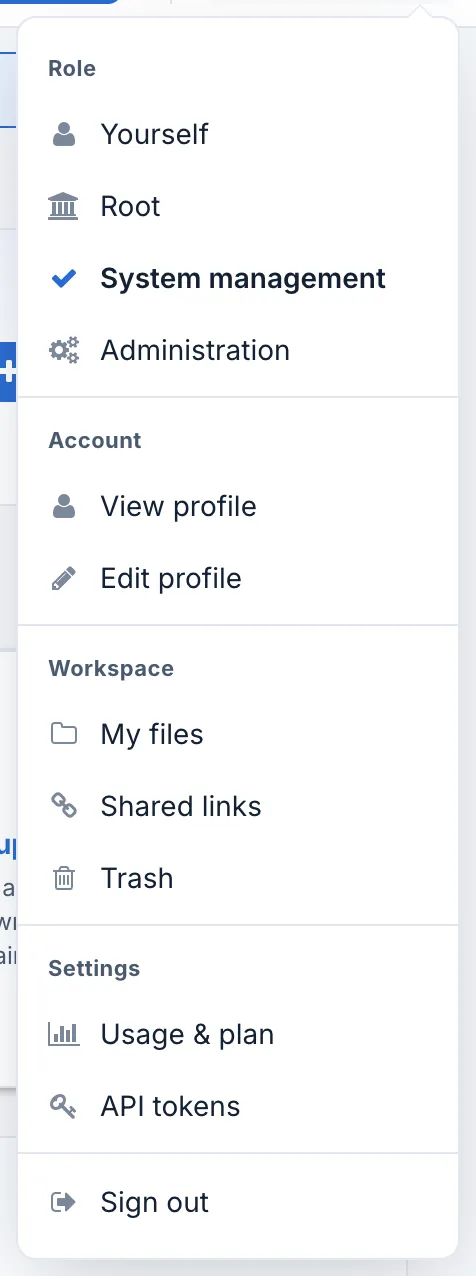 **The Administration area,** in System management, has an **Account** page for each person: their handles, their plan, and how much of each limit they use. From there System management can give a plan free of charge (until a date, or for good), set a limit for one account, confirm an email, and grant or revoke roles. **Sign-ups**, **Plans** and the **Audit log** sit beside it. How each part is built is in Running Knowen, which only role holders can open. **Everything is logged.** Every change made in a role goes to an audit log under the real person's name, kept three years. **What they see.** System management sees an account's email, all its handles, its plan and its usage counts, so it can help with sign-in and limits. It never sees private content: a private graph stays readable only by its members. Root reads what any member reads, plus the Reviewing queue. **How it is built.** A role is a grant to a person, revoked rather than deleted. Switching to Root signs the browser session in as the Root account and remembers the person; signing out ends both. The API never switches roles. The audit log is append-only. **In development:** suspending accounts and deleting them on request, two-factor sign-in for role holders, Root's content tools (hide, lock, transfer ownership), and reminders about proposals waiting 30 days. **For role holders:** [Running Knowen](dna:running-knowen/nodes/29590) explains how all this is built. The link opens only for people who hold a role. --- ⏎ **Part of** [Your account and identity](/nodes/29515) and [Who owns what](/nodes/29577): all its parents are equal.⏎ ⏎ # Parents * Your account and identity * Who owns what
Feedback00
No feedback yet. Say whether this change improves the node.
Sign in to add a new comment.